Buy werkstoff.eu ?
We are moving the project
werkstoff.eu .
Are you interested in purchasing the domain
werkstoff.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy werkstoff.eu ?
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
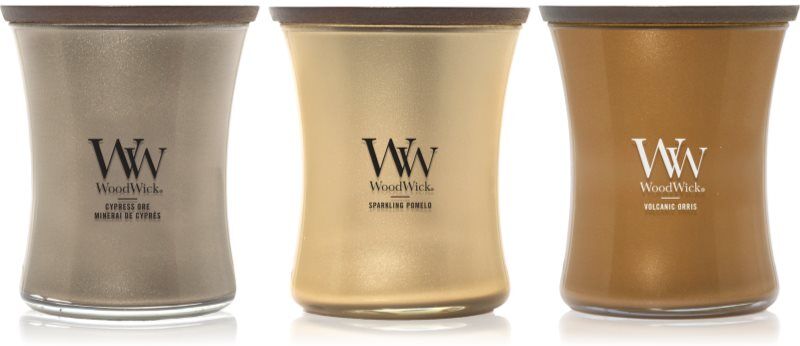
Woodwick Precious Metals Trio Pack gift setWoodwick Precious Metals Trio Pack, 1 pc, Gift Sets Home Scents, Fill your home with a gorgeous fragrance or surprise your loved one with a lovely gift. Woodwick Precious Metals Trio Pack gift set will be a sure hit in both cases. A carefully selected home fragrance will instantly create a calm, relaxing atmosphere and make any home feel lovely and cosy. Characteristics: a warm fragrance gently crackles while burning, thus creating a cosy atmosphere designer packaging ideal as a gift long burning time a luxurious accessory for any room gives the room a distinctive character fills the room with a pleasant aroma quickly fills the entire room with fragrance encourages a sense of calm and well-being creates a pleasant environment for relaxation The set contains: Woodwick Precious Metals Sparkling Pomelo scented candle 275 g Woodwick Precious Metals Cypress Ore scented candle 275 g Woodwick Precious Metals Volkanic Orris scented candle 275 g Ingredients: with soy wax wooden wick How to use: Follow the instructions on the package. Always let the candle burn until the surface completely melts to prevent an unwanted hollow in the wax from forming.55,10 £*Shipping: 3,99 £Secure redirect to the provider

-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **

How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
Top-Angebote
Products related to Tpm:
-
Aurora Eco Nation 9.5" Plush Pig for Kids - Eco-Friendly Toy Made from Recycled Plastics and Natural MaterialsEmbark on a journey into the heartwarming world of Aurora Eco Nation, a captivating collection of soft toys thoughtfully crafted from recycled plastics and natural materials. Among these eco-conscious treasures, the Eco Nation Pig Soft Toy shines as a symbol of sustainability and cuddly charm. Key features of this soft toy include Aurora's commitment to eco-friendliness, where each toy is created using recycled plastic bottles, from the outer plush material to the fiber fill. The pig's embroidered eyes ensure safety and environmental responsibility. This soft toy captures the endearing essence of a pig and measures 9.5 inches, making it a substantial and welcoming plush companion. The hangtag is recyclable and designed to resemble a plastic bottle, showcasing the brand's dedication to sustainability.12,41 £*Shipping: 3,95 £Secure redirect to the provider
-
Woodwick Precious Metals Trio Pack gift setWoodwick Precious Metals Trio Pack, 1 pc, Gift Sets Home Scents, Fill your home with a gorgeous fragrance or surprise your loved one with a lovely gift. Woodwick Precious Metals Trio Pack gift set will be a sure hit in both cases. A carefully selected home fragrance will instantly create a calm, relaxing atmosphere and make any home feel lovely and cosy. Characteristics: a warm fragrance gently crackles while burning, thus creating a cosy atmosphere designer packaging ideal as a gift long burning time a luxurious accessory for any room gives the room a distinctive character fills the room with a pleasant aroma quickly fills the entire room with fragrance encourages a sense of calm and well-being creates a pleasant environment for relaxation The set contains: Woodwick Precious Metals Sparkling Pomelo scented candle 275 g Woodwick Precious Metals Cypress Ore scented candle 275 g Woodwick Precious Metals Volkanic Orris scented candle 275 g Ingredients: with soy wax wooden wick How to use: Follow the instructions on the package. Always let the candle burn until the surface completely melts to prevent an unwanted hollow in the wax from forming.55,10 £*Shipping: 3,99 £Secure redirect to the provider
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
Similar search terms for Tpm
-
Drop Dash Deals Toyota Tundra Front Left Driver Side Bumper Cover Replacement OEM Fit Plastics Toyota Tundra Front Left Driver Side Bumper Cover Replacement OEM Fit PlasticsStep into confidence every time you hit the road with this highquality 1 pc of Toyota Tundra bumper cover designed for drivers who refuse to compromise on protection or style. This front left driver side cover fits 2022 and 2023 Tundra models...239,97 $*Shipping: 0,00 $Secure redirect to the provider
-
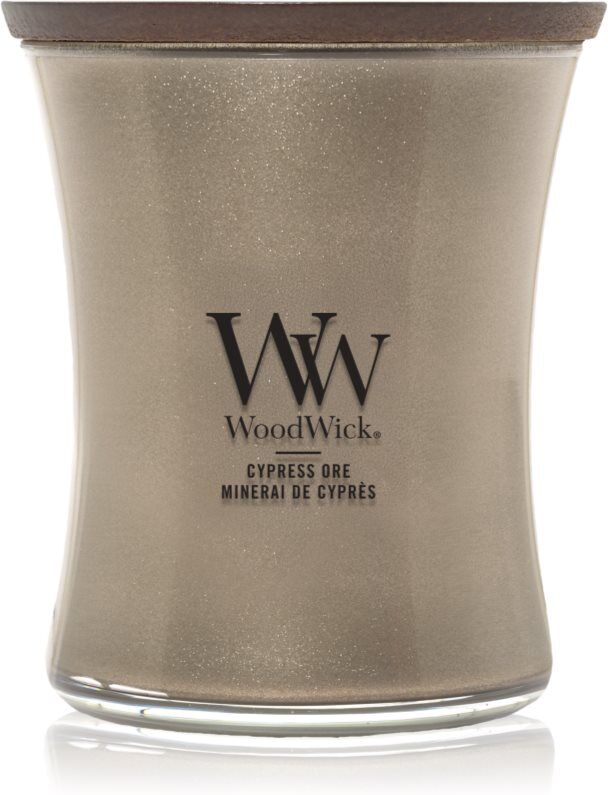
Woodwick Precious Metals Cypress Ore scented candle 275 gWoodwick Precious Metals Cypress Ore, 275 g, Scented Candles Home Scents, The mood and atmosphere of a space can be changed instantly by fragrance. The Woodwick Precious Metals Cypress Ore scented candle fills your home with fragrance and creates a pleasant atmosphere for relaxation and those everyday moments spent on your own or with loved ones. The flickering, quietly crackling flame also adds a warm, soothing atmosphere to the room. Characteristics: a woody fragrance Ingredients: with soy wax How to use: Always let the candle burn until the surface completely melts to prevent an unwanted hollow in the wax from forming.19,60 £*Shipping: 3,99 £Secure redirect to the provider
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.